Web Application Security Demo
The same full-stack app built twice — intentionally vulnerable, then hardened.
Tech stack
- React
- TypeScript
- Vite
- Drizzle ORM
- PostgreSQL
- Zod
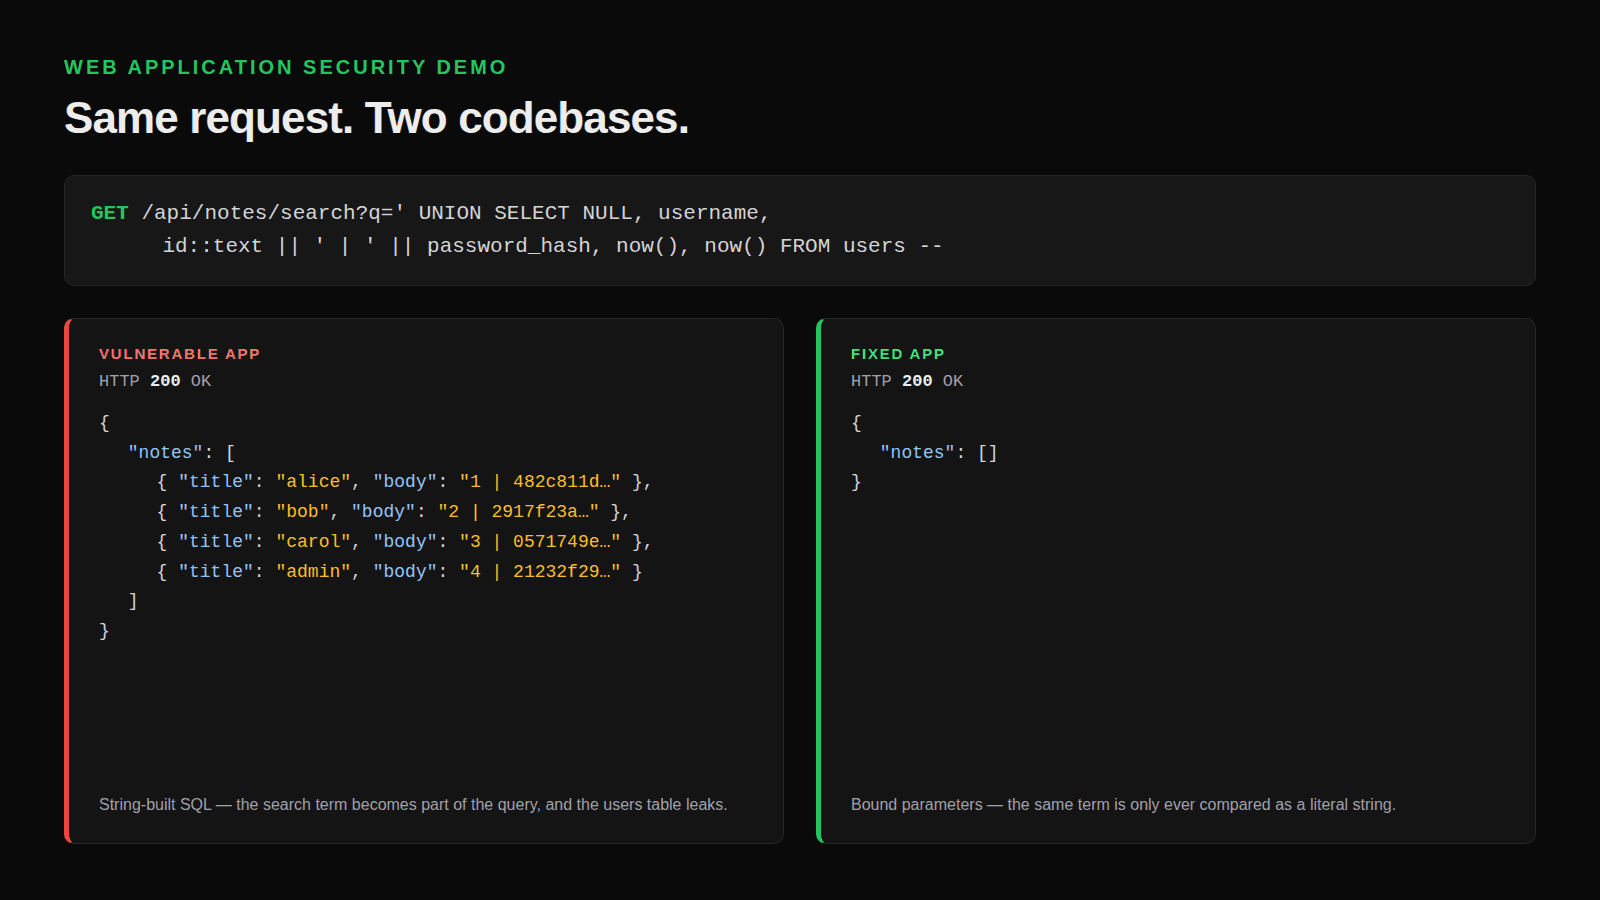
A cookie-session login and notes CRUD app implemented as two variants: one with realistic, intentional web vulnerabilities and one hardened with industry-standard practices. Every flaw is documented as flaw to exploit to fix to principle, with runnable exploit requests and an in-app attack console that fires real requests at the API.
Features
- One cookie-session login and notes CRUD app built twice: an intentionally vulnerable variant and a hardened one with the same features.
- Six vulnerability classes mapped to the OWASP Top 10 — SQL injection, broken authentication, IDOR, stored XSS, missing CSRF protection and verbose errors.
- Per-flaw write-ups taking each issue from exploit to fix to underlying principle, backed by runnable exploit requests.
- In-app attack console that fires real requests at the vulnerable API.
- Vulnerable app runs only behind a shared-password gate, holds fake seeded data, carries an insecure-demo banner and re-seeds on a schedule.
- Both deployments rate-limited at the edge; databases and secrets fully isolated between the two apps.
About this project
One small app — cookie-session login plus notes CRUD — built twice. apps/vulnerable carries realistic, intentional web vulnerabilities; apps/fixed has the same features hardened with standard practices. The write-ups take each flaw from exploit through fix to the underlying principle, backed by runnable exploit requests.
The vulnerable app is a deliberately insecure teaching demo. It holds only fake, seeded data; the unsafe behaviour is off by default and runs only behind a shared-password gate; its database and secrets are fully isolated from everything else; every page carries an insecure-demo banner; both deployments are rate-limited at the edge; and the vulnerable database is re-seeded on a schedule.
The hardened app is the live demo. The gated vulnerable deployment lives at cybersecurity-vulnerable.vercel.app.